Fraud Investigations
Investigate diverted funds or goods, false documents, procurement and expense fraud, supplier collusion and online scams. We gather evidence to clarify the facts and inform decisions.
Explore the serviceIdentify how sensitive information could be exposed.
Assess information flows, relationships and sensitive environments to understand strategic exposure and privacy vulnerabilities.
Scope and deliverables defined for your business.
BARUCH / ANALYSIS AND EXECUTIONExposure assessment
01 / When it makes sense
There are signs of improper information acquisition or environments need assessment for listening devices and hidden cameras.
Leadership, Legal and teams responsible for strategic information, negotiations or sensitive environments.
In practice
Hypothetical examples of situations where this solution can help your organisation.
Information from a proposal still under discussion reaches people outside the intended group. The business needs to assess document flows, access and environments to decide which controls to review and which indicators require further investigation.
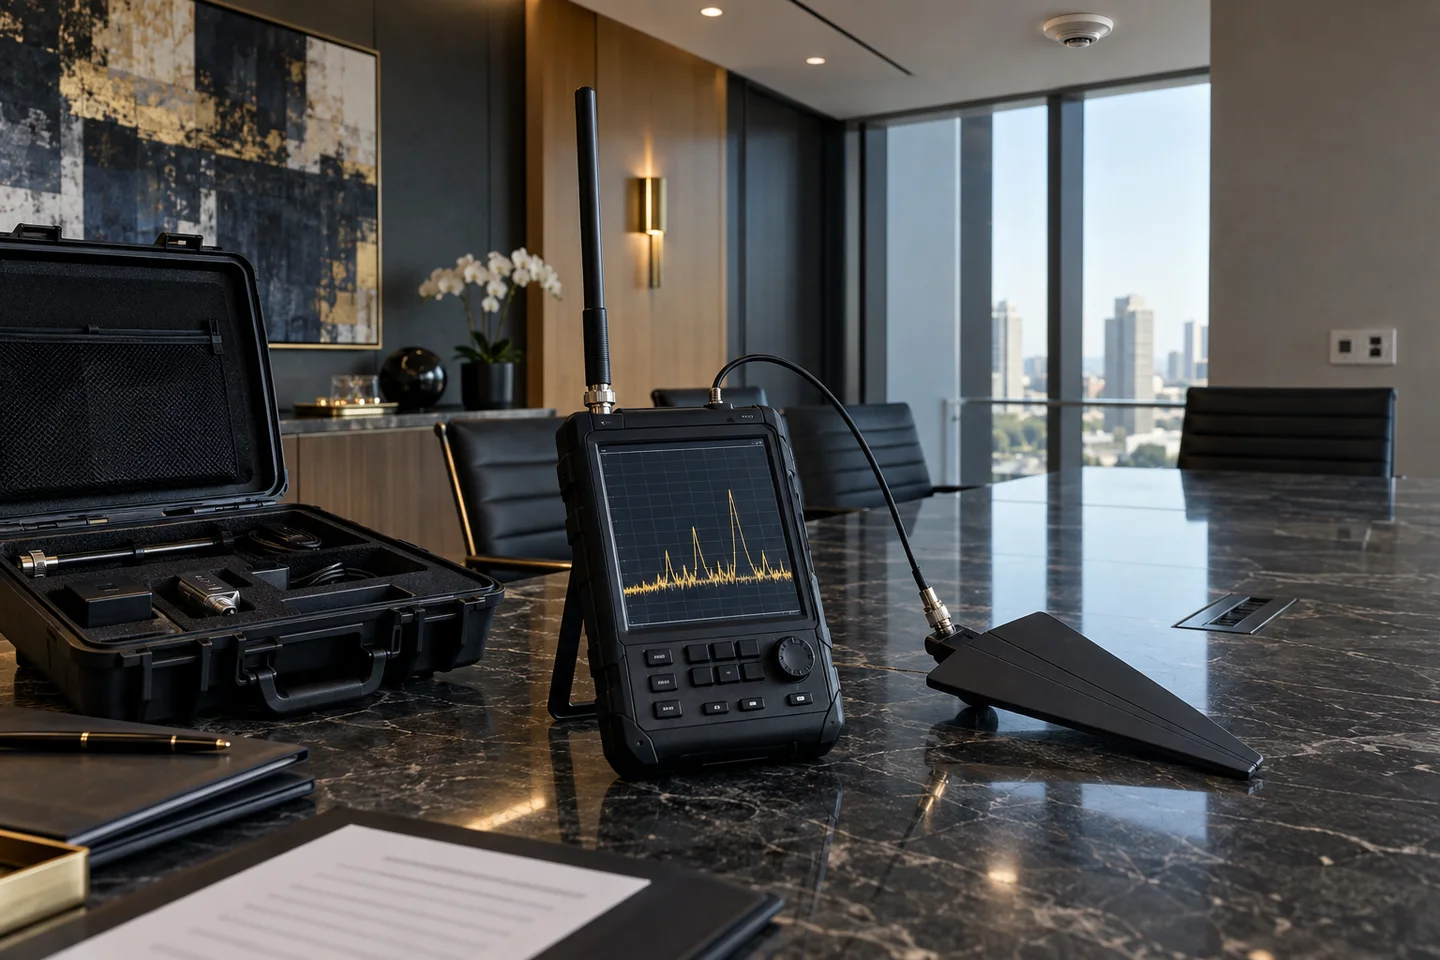
A defined environment needs physical inspection and electronic sweeps to check for possible listening devices or hidden cameras.
Indicators of improper access to or use of strategic knowledge require assessing flows, relationships and organisational weaknesses.
02 / From analysis to decisions
03 / Your deliverables
Choose an option to see an example deliverable.
Swipe the options to see more deliverables →
Findings on flows, access and relationships that may enable improper acquisition or use of information.
Illustrative structure. No client data or results.
Documents concerning a fictional negotiation.
Sensitivity agreed with the companyMaterials circulate among internal roles and third parties.
Access and purpose to checkPost-project access review is not defined.
Illustrative organisational findingThe assessment examines flows and vulnerabilities through lawful means without presuming espionage or covert access.
Content and depth are defined according to your project scope.
Inspection records and environmental findings when the TSCM module is included in scope.
Illustrative structure. No client data or results.
| Focus | Illustrative example | Interpretation / next step |
|---|---|---|
| Authorised areas | A fictional meeting room and areas included in the project. | Technical sweep where agreed |
| Inspection record | Conditions and procedures applied to the environment. | Date and conditions documented |
| Finding to check | An unidentified item requires checking with the owner. | Does not establish a listening device |
A sweep describes the environment and conditions examined. No findings do not constitute a permanent privacy guarantee.
Content and depth are defined according to your project scope.
Control priorities and supporting information for further enquiries by responsible teams.
Illustrative structure. No client data or results.
Agree who needs access to each sensitive material.
Information ownerClarify the items and conditions noted during inspection.
Where inspection is in scopeRecord criteria for reviewing access and use of environments.
Agreed prioritiesRecommendations connect exposure to controls without portraying the service as absolute protection against leaks.
Content and depth are defined according to your project scope.
Which decision should this deliverable support?
Tell us what you need04 / The work
Explore the stages of the work. The scope starts with your context, available information and the decision your business needs to make.
We identify strategic information, relevant flows and relationships, and the environments requiring technical assessment.
We assess organisational weaknesses and, where agreed, combine physical inspections and electronic sweeps of the environments.
We consolidate findings with context and recommendations to reduce vulnerabilities and pursue relevant lines of enquiry.
05 / A tailored scope
Combine the capabilities your challenge requires.
We assess information flows, access and relevant relationships, examining indicators through lawful methods and identifying organizational weaknesses that could enable exposure or misuse of information.
Deliverable: An exposure assessment and recommendations to protect strategic information, with contextualized findings, control priorities and supporting material for further investigation by the teams responsible.
We combine electronic sweeps and physical inspections of the agreed environments.
Deliverable: A technical findings report and recommendations to reduce vulnerabilities.
Contact Baruch
Chat on WhatsApp or prepare your enquiry using the form below.
Let's talk
Add your details and a short description to prepare your enquiry by email or WhatsApp.